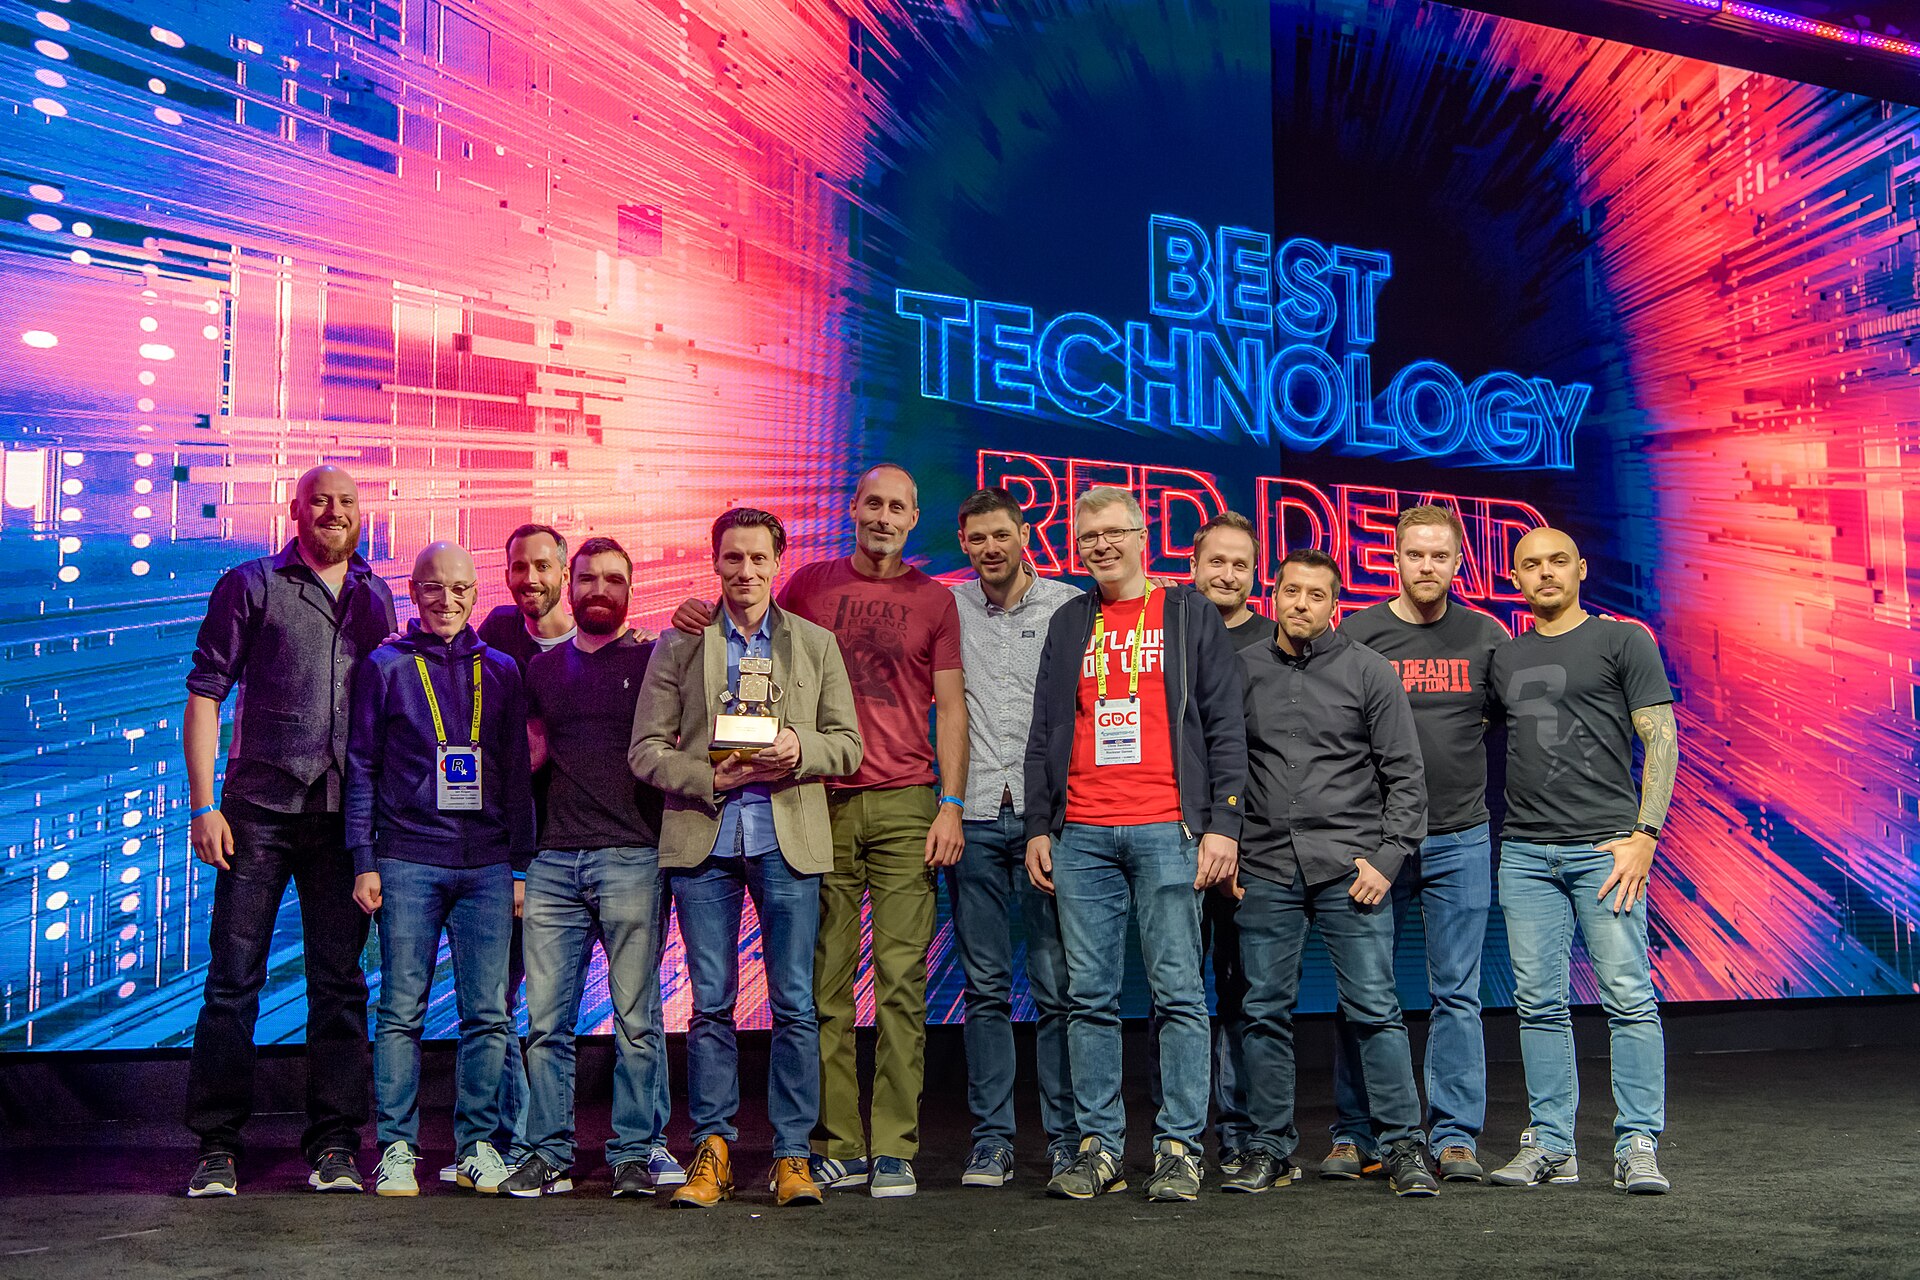
Rockstar Games staff accept the Best Technology award at the 2019 Game Developers Choice Awards. Archive photograph of the studio’s team, not of Kurtaj or the criminal proceedings. Archive photo by Official GDC (CC BY 2.0).
Arion Kurtaj, the hacker who released early Grand Theft Auto VI footage, pleaded guilty on Monday, November 16, bringing a long-running cybercrime case to a new legal stage just days before the game's scheduled launch. The Crown Prosecution Service said the 21-year-old, formerly of Oxfordshire, admitted offences arising from attacks on Rockstar Games, BT/EE, Revolut and Uber.
Sentencing is scheduled for November 23 at Woolwich Crown Court. The CPS announcement lists three computer-impairment offences, fraud, unauthorised access with further criminal intent, and possession of a mobile phone in prison. Prosecutors said Kurtaj took and released 90 gameplay videos under the name TeaPotUberHacker and threatened to release source code.
The famous game explains much of the public interest, but it is only one part of the case. The offences concern access to companies' systems, the treatment of information obtained through that access and the disruption that followed. A leaked clip is the visible product of a breach; it is not a complete account of its consequences.
For Rockstar and its parent company, Take-Two Interactive, the timing is particularly notable. Take-Two's November 9 filing still lists Grand Theft Auto VI for release on November 19, 2026, on PlayStation 5 and Xbox Series X|S. Monday's court development concerns the 2022 intrusion, rather than a newly announced compromise of the finished game.
Why the guilty pleas are a new development in an old case
Readers who remember reports about Kurtaj in 2023 may reasonably wonder why he is back in the news. The answer lies in the unusual form of the earlier proceedings. At that time, psychiatrists had assessed him as unfit to stand trial. The jury was asked whether he had carried out the alleged acts, rather than to return the ordinary verdict of guilty or not guilty, the Associated Press reported.
That procedural distinction is essential to understanding the chronology. A finding about whether acts occurred in such proceedings is not interchangeable with a conventional criminal trial in which guilt is determined. Reporting the earlier hearing simply as a normal conviction, followed by an unexplained second conviction, would obscure why the case developed as it did.
In July 2026, GamesRadar reported, citing BBC cyber correspondent Joe Tidy, that Kurtaj had left the secure hospital where he had been held and was in prison awaiting a conventional trial. The change was reported as part of the legal process. It does not give outside observers a basis to make their own assessment of his mental health or to speculate about the clinical decisions behind it.
Monday's guilty pleas now supply the immediate news. Sentencing remains a separate event, and the punishment has not been announced in advance of the November 23 hearing. A report can describe the admitted offences without pretending to know what the court will decide about the appropriate sentence.
The statutory language also explains why “leaking a video game” is an incomplete description. The CPS's Computer Misuse Act guidance distinguishes unauthorised access with an intention to commit or facilitate another offence from unauthorised acts intended, or recklessly liable, to impair a computer's operation. The law concerns interference with systems and criminal intent, not merely whether the resulting material interests an audience.
For a general reader, the practical distinction is between receiving information made public by someone else and illegally obtaining it from a protected system. The case concerns the latter conduct and related offences. The popularity of the material does not change the character of the access through which it was acquired.
The leak exposed unfinished work and a company's internal risk
Take-Two's September 2022 securities filing acknowledged that an unauthorised third party had accessed and downloaded confidential Rockstar information, including early development footage of the next Grand Theft Auto. The company said it had taken steps to contain the incident and did not then anticipate disruption to current services or a long-term effect on development timelines.
That contemporaneous statement establishes what the company said at the time. It should not be converted into a claim that responding to the intrusion required no work, or that every later scheduling decision can be traced to it. A studio can continue development while also investigating a breach, restoring confidence in access controls and deciding what information has been exposed.
Unfinished development footage also serves a different purpose from a trailer. A working build may contain temporary visual elements, diagnostic information or experiments that do not represent the eventual product. Its value to developers comes from testing and iteration. Showing it outside that setting can invite a public judgment of material never prepared as a public demonstration.
The damage question therefore extends beyond a spoiler about a fictional location or character. Confidential work can embody years of collaboration, commercially valuable decisions and information about a company's production process. An organisation has to establish what was taken before it can judge the significance of disclosure. That uncertainty consumes attention even when public services continue to run.
The gap between 2022's stolen development clips and the 2026 release schedule is also a useful chronological safeguard. Monday's plea is not evidence that the current retail build has been altered, that player accounts have been compromised or that launch services will be unavailable. Those would be separate claims requiring their own evidence.
Take-Two's latest filing describes a business built around Rockstar Games, 2K and Zynga, with products across console, PC and mobile platforms. Within that larger operation, a major release is both creative work and a substantial commercial commitment. The case illustrates why protection of internal systems belongs to the production process rather than sitting outside it as a purely technical concern.
The Uber record shows why identity and access matter
Uber's September 2022 incident account offers a detailed view of the kind of access problem that confronted companies during that period. The company said a contractor's account had been compromised, followed by access to additional employee accounts and internal tools. It described repeatedly generated login-approval requests, one of which was eventually accepted.
Uber said it blocked or reset affected accounts, disabled some internal tools, rotated access keys and required renewed authentication as systems were restored. It also said its investigation had not found access to the production systems powering its public apps or to the databases holding sensitive user information such as trip histories and payment details.
Those statements should be read with their date and scope attached. They were Uber's account of its investigation, not a universal finding about every company in the criminal case. They nevertheless explain a basic security problem: possession of a valid-looking account can become a route into several connected tools, and responding may require changes across that chain.
The lesson is not that additional login protections are pointless. It is that their design and the surrounding procedures matter. A security control that depends on a tired employee correctly interpreting an unexpected prompt has different strengths and weaknesses from one that binds authentication more closely to a legitimate service and device.
The U.S. Cyber Safety Review Board's review of Lapsus$ and related threat groups called for stronger access controls and authentication, including phishing-resistant methods. It also addressed the relationships among organisations, telecommunications providers and law enforcement. Its recommendations treat these incidents as a problem of systems and incentives, rather than assuming that the purchase of one new security product can resolve every weakness.
Account recovery deserves the same scrutiny as the initial login: a strong front door is less effective if an identity can be reset through a weaker process.
That wider perspective avoids blaming a single worker for a failure an organisation has to anticipate. Employees need clear ways to reject and report suspicious requests, and help desks need reliable procedures for identity checks and account recovery. Limiting unnecessary privileges can also reduce the reach of one compromised identity. These are questions of institutional design as much as individual vigilance.
The public interest lies beyond the mythology of a notorious hacker
The fame of Grand Theft Auto makes this a story that reaches people who might never read a conventional cybercrime report. That attention can be useful if it illuminates the work of investigators, the vulnerabilities of connected systems and the costs imposed on employees and customers. It becomes less useful when the case is reduced to admiration for an intruder's ingenuity.
The National Crime Agency's Cyber Choices program makes a distinction between unlawful intrusion and legitimate opportunities for technically skilled young people. Research and security testing can be valuable when conducted with permission. The decisive boundary is authorisation, not whether the person involved is talented or whether the target is a large corporation.
There is also a reporting obligation to avoid letting a medical history stand in for an explanation of offending. The procedural record is relevant because it explains the case's progress. It does not justify generalisations about other people with the same diagnosis, and it does not remove the need to describe the admitted conduct precisely.
As November 23 approaches, the next concrete development will be the court's sentence. The confirmed position now is that Kurtaj has pleaded guilty, the offences extend beyond Rockstar, and the leaked material belonged to an intrusion from four years earlier. For the games industry, the lasting issue is how to protect creative work while thousands of people and tools collaborate on it. For the justice system, the case has reached a conventional admission of guilt after an unusual procedural history. Both stories are larger than the 90 clips that first brought it to public attention.